Changing a compromised service password can stop the very systems you're trying to protect. The trouble is often a forgotten dependency still using the old value. Discovering those dependencies and previewing the change plan makes rotation a controlled operation instead of a guessing game.
The hard part isn't generating a new secret. It's finding every place that depends on the old one and changing those places in a controlled order. During an incident, learning that dependency map from production failures is especially painful.
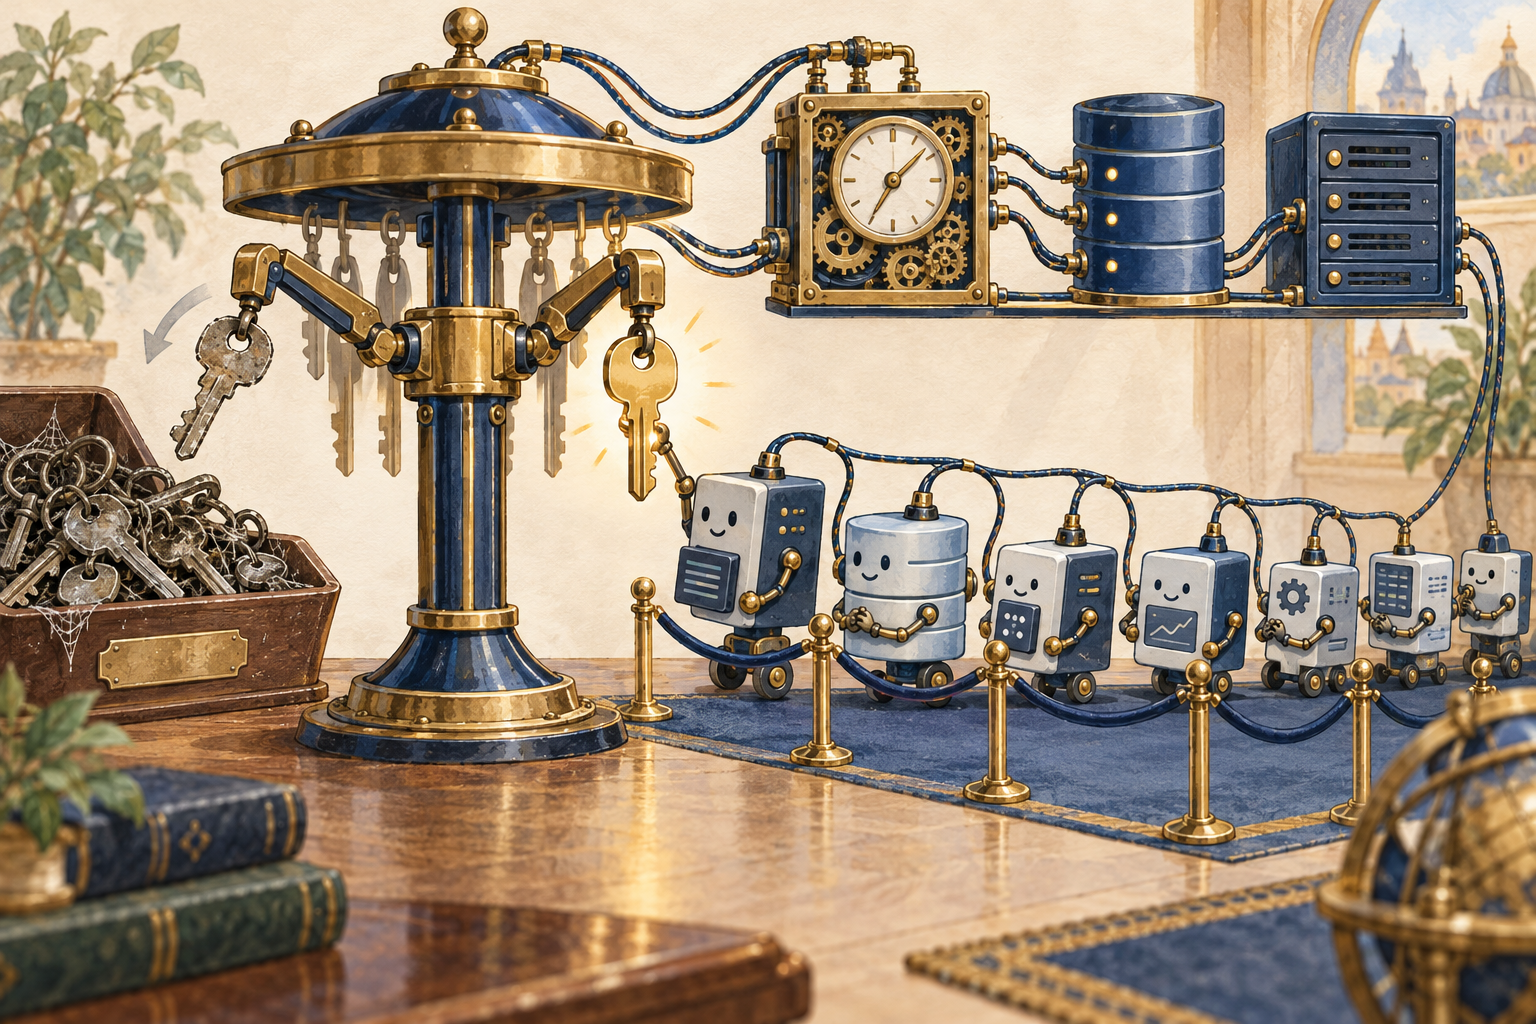
AIC Enterprise Privilege Suite™ discovers supported credential dependencies and builds a change plan. That can include Windows services, scheduled tasks, IIS application pools, and COM+ or DCOM uses, with additional supported configuration dependencies included in the plan. The operator can preview the work before applying it.
The workflow changes the target credential, propagates the new value to the configured dependencies, restarts dependent services in order, and verifies sign-in. The audit trail preserves the steps. Test application health as well: successful authentication doesn't by itself prove that every business process recovered.
The dependency picture also exposes concentration of risk. One service account used across many hosts gives a stolen credential more reach. AIC's credential-dependency discovery shows supported uses of the account. IT can use that dependency map to plan separate service identities and preview the rotation work for each.
Inventory quality matters. Unknown dependencies and unsupported applications need investigation before a production rotation. Start with a representative nonproduction service and include rollback and recovery in the exercise.
Start with a documented rotation recipe on a representative test system. AIC's free product guidance and training help your team learn the sequence without mastering every credential type at once. Reusing a tested plan for comparable systems can reduce recurring work. The goal is to make rotation a routine operation instead of a project everyone puts off.
Bring the credential your team is afraid to change. We can demonstrate dependency discovery and a rotation plan against supported systems, then identify what must be verified in your environment before you run it. We welcome the dependency nobody knows how to handle. Your feedback helps us improve dependency discovery, rotation plans, and recovery instructions for the people who run those changes.
Explore PIM dependency discovery and credential propagation · Request a Demo
Background: NIST control assessment methodology