Personal password and document vault
Each person has a vault for the passwords and documents they use at work. The vault holds logins, secure notes, and files. People share items with named people and with collaboration groups. The same suite still vaults, rotates, and propagates administrator and service credentials. Those privileged credentials stay in a separate vault.
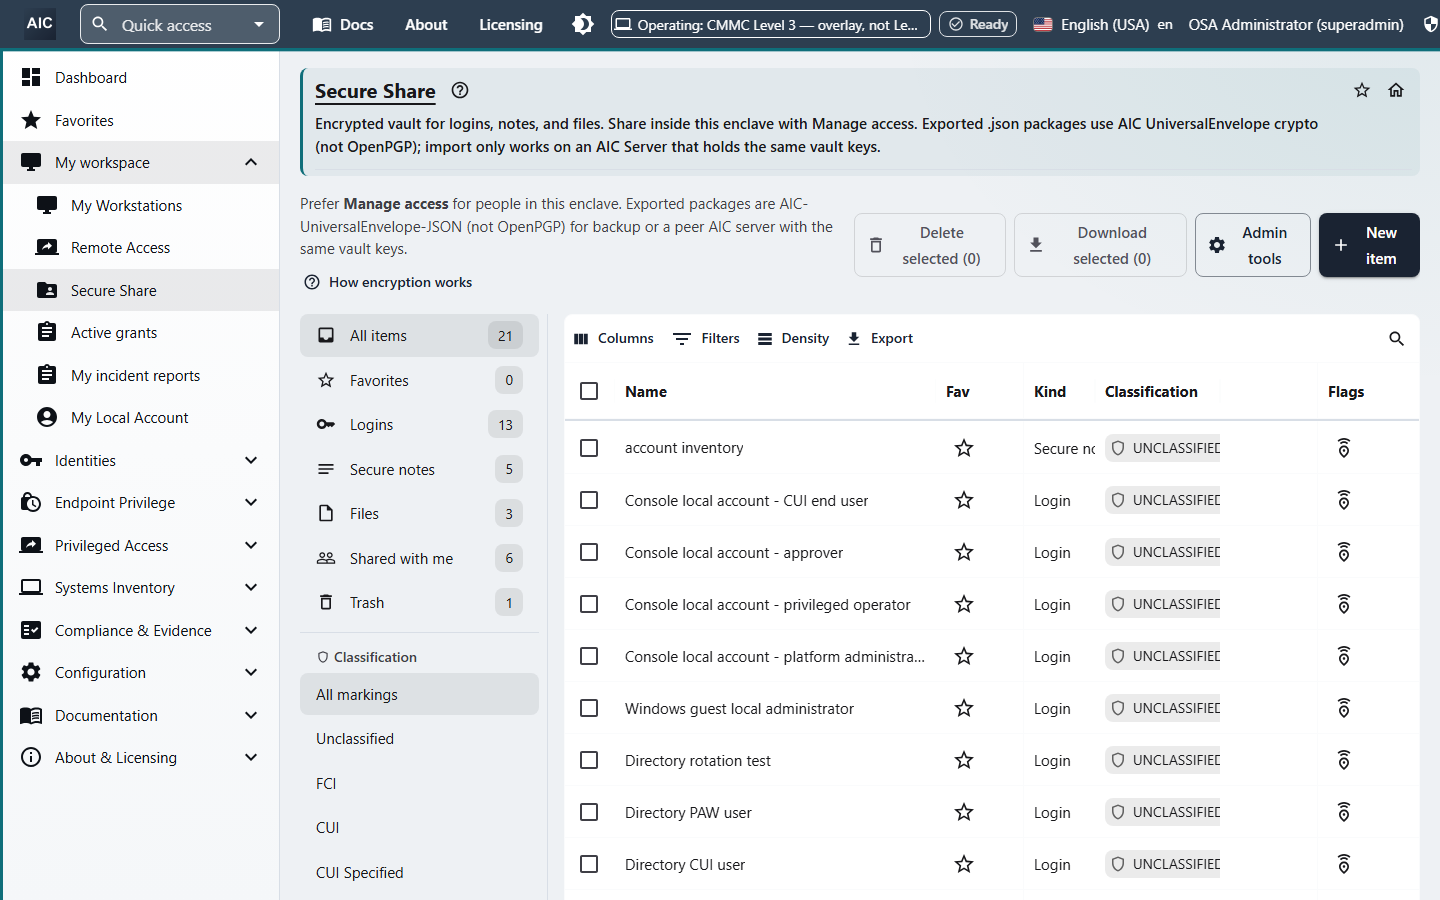
The console name for this vault is Secure Share. Personal password and document collaboration is included with named users on every AIC CMMC Complete package (Cybersecurity Maturity Model Certification, CMMC) and every AIC Enterprise Privilege Suite package. There is no separate personal-vault package. AIC Enterprise Privilege Suite is priced by quote.
Feature pages
- Password manager for one person covers logins, the generator, notes, files, favorites, search, and trash.
- Sharing with people and groups covers access lists, groups, and revoke.
- Encryption and classification covers customer-held keys, markings, and export rules.
What a person can store
| Item | What it holds |
|---|---|
| Login | User name, password, one website address per line, notes, and custom fields. Custom fields can be text, hidden, or yes/no. |
| Secure note | Text the person wants kept with the vault. |
| File | A document stored as a vault item. Each file is limited to 5,242,880 bytes. |
A person can mark an item as a favorite, search the vault, and move an item to trash and restore it. Copying a revealed password or note to the clipboard clears that clipboard after 30 seconds.
Password and passphrase generator
When a person creates a login, the vault can generate a password or a passphrase.
- A password can be 12 to 128 characters, with lowercase, uppercase, digits, and symbols, and with ambiguous characters left out.
- A passphrase can be 3 to 10 words, with a separator, optional capitalization, and an optional digit.
- Saving a login can refuse a password that appears in a known-breach list.
Sharing and classification
Sharing uses an access list. A person or a group can be granted list, read, write, share, delete, or export on an item. Revoking access re-wraps the item so the removed party no longer holds a usable copy of the key.
Each item can be marked Unclassified, Federal Contract Information (FCI), Controlled Unclassified Information (CUI), or CUI Specified. FCI and CUI stay encrypted. A clear export of CUI is refused. An encrypted export of the person's own package is available.
Encryption
Items are encrypted at rest under keys the customer holds: software keys, a hardware security module, or the customer's own cloud key service. The server decrypts an item when the person reveals it, downloads a file, or an approved break-glass action runs. That is managed encryption inside the customer's environment. It is a different design from a vault that only the person's device can open.
Server cryptography uses the AWS-LC Federal Information Processing Standards (FIPS) module, Cryptographic Module Validation Program certificate 4759, for the module boundary. The certificate covers that module.
What ships, and what is planned
| Capability |
|---|
| Logins, secure notes, and files |
| Password and passphrase generator |
| Breach check when a password is saved |
| Favorites, search, and trash |
| Share with named people and groups |
| FCI and CUI marking, with clear export of CUI refused |
| Encrypted at rest on hardware the customer owns, including an air-gapped system |
Planned
- Browser extension and autofill
- Phone and desktop vault applications
- Authenticator codes and passkeys stored as vault items
- Payment cards and identity records
- Import from another password manager
- Personal folders in the vault
Privileged password rotation, session recording, and endpoint elevation are separate capabilities. They ship today. They are not features of this personal vault. See Capabilities and What is password management.
Where it sits in the kit
Each named user has the vault, including sharing, on AIC CMMC Complete Level 1, Level 2, and Level 3, and on AIC Enterprise Privilege Suite Team, Standard, Enterprise, Premium, and Platinum. Level 1, Level 2, and Level 3 also include governed mail. The privileged credential vault, recorded sessions, and endpoint elevation are part of Level 2 and Level 3.
See CMMC pricing | See capabilities | Request a demo
Copyright 2026 Analog Informatics Corporation. All rights reserved.
For more information about Analog Informatics Corporation, please go to analoginfo.com.