Encryption and classification for the password vault
Analog Informatics Corporation encrypts each Secure Share item under keys the customer holds. Secure Share is the personal password and document vault for logins, secure notes, and files. This page is the security view: where the keys live, when the server decrypts an item, and how classification changes what may leave the vault. Saving and finding items is on Password manager for one person. Grants are on Sharing with people and groups.
Personal password and document collaboration is included with named users on every AIC CMMC Complete package (Cybersecurity Maturity Model Certification, CMMC) and every AIC Enterprise Privilege Suite package. There is no separate personal-vault package. AIC Enterprise Privilege Suite is priced by quote.
Keys the customer holds
Items are encrypted at rest. New writes use the active key. The customer can keep that key as software, on a hardware security module (HSM), or in the customer's own cloud key service. Software keys and an HSM can both be live, so a move from one to the other does not stop reads.
The same design runs on hardware the customer owns, including an air-gapped system that is not connected to the public network. The vault is not a hosted-only password service.
When an item is decrypted
The server decrypts an item when an authorized person reveals it, downloads a file, or an approved break-glass action runs. That is managed encryption inside the customer's environment. It is a different design from a vault that only the person's device can open. The server can open an item for those authorized actions.
Server cryptography uses the Amazon Web Services LibCrypto (AWS-LC) Federal Information Processing Standards (FIPS) module, Cryptographic Module Validation Program certificate 4759, for the module boundary. The certificate covers that module.
Classification on every item
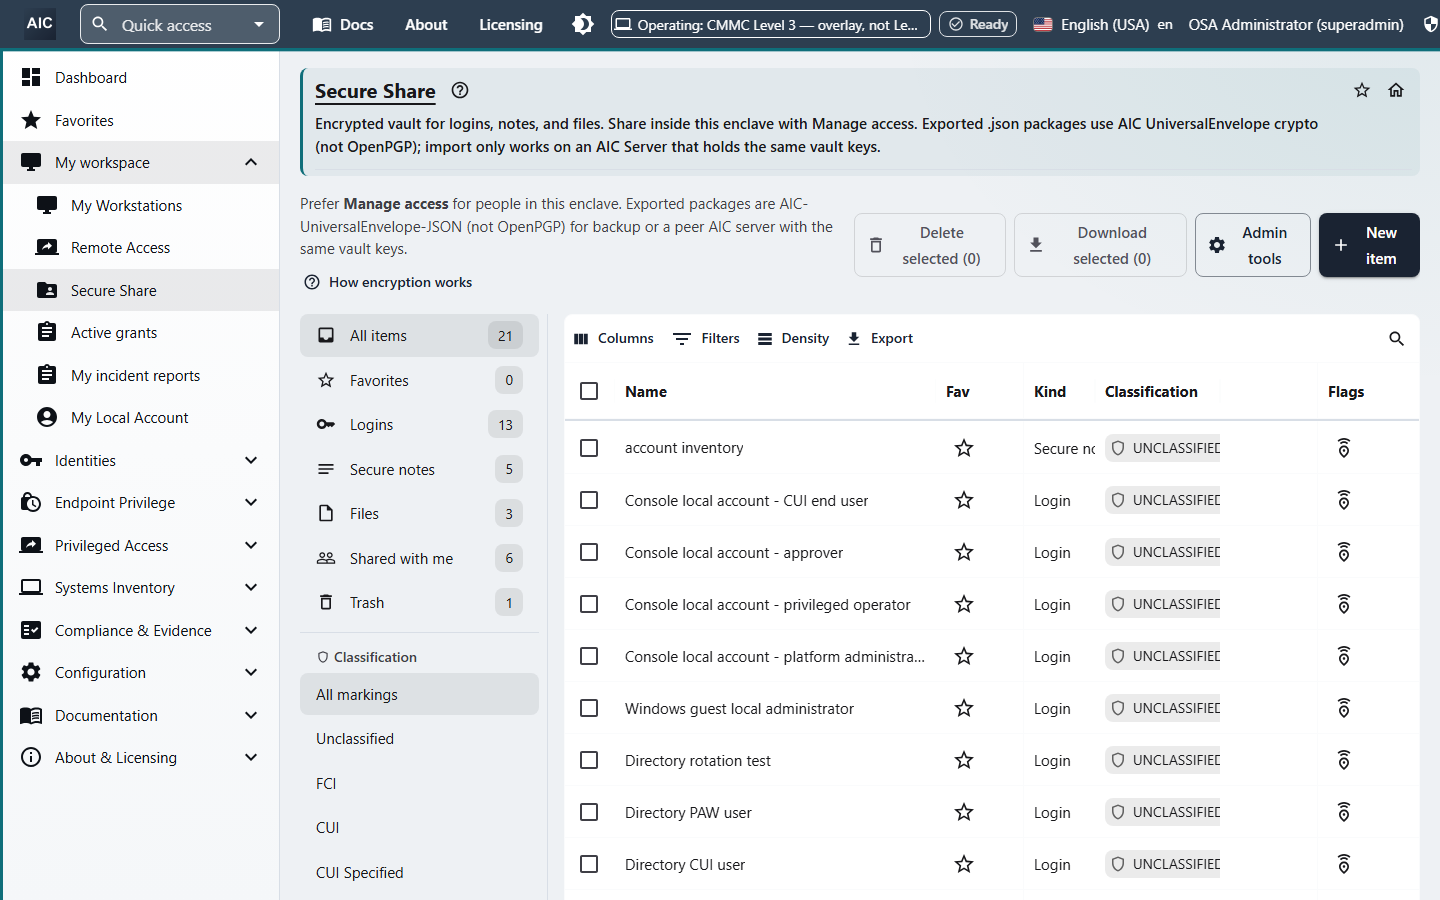
Each item carries a marking. The markings a person can pick are the ones the organization has turned on. That set always includes Unclassified, Federal Contract Information (FCI), Controlled Unclassified Information (CUI), and CUI Specified. When the organization turns on wider government or corporate families, those markings use the same picker. The catalog is described on Data classification and national markings.
FCI and CUI stay encrypted. A clear export of CUI is refused. An encrypted export of the person's own package is available. Write permission on a shared item includes editing the classification.
A classification filter on the left side of the vault limits the list to one marking.
Related capabilities and planned features
Privileged credential rotation uses a separate vault. Session recording and endpoint elevation are separate capabilities.
The shipping design keeps the keys with the customer and lets the server decrypt for an authorized reveal, download, or break-glass action.
Planned
- Browser extension
- Phone and desktop vault applications
What ships
| Capability |
|---|
| Encrypted at rest under customer-held software keys, an HSM, or the customer's cloud key service |
| Software keys and an HSM live at the same time |
| Air-gapped operation |
| Decrypt for reveal, download, and approved break-glass |
| FCI and CUI marking, with clear export of CUI refused |
| Encrypted export of the person's own package |
Password manager for one person | Sharing with people and groups | Vault overview | Request a demo
Copyright 2026 Analog Informatics Corporation. All rights reserved.
For more information about Analog Informatics Corporation, please go to analoginfo.com.